








































Three people discuss a chart on a laptop screen at a table.

Virtline certificate

Virtline ISO 27001 certificate

View the certificate for Virtline’s information security management system, issued by TÜV NORD Polska. Download the document to check its number, scope and validity dates.

Trusted by

Companies and institutions that need stable IT.

  • AdAc
  • Baseline
  • BTW
  • Charlie
  • Dako
  • EVO
  • FTH
  • IFJ
  • MAEM
  • Banki Spółdzielcze BPS
  • PJG
  • Spinel Trade
  • Suder
  • Ziko Apteka
  • Aforti
  • Base Finance
  • CADM
  • Consol
  • Deka Trans
  • Ferro
  • GATE
  • Igoria Trade
  • Magnet Audit
  • Novacura
  • Przetargi
  • Streamsoft
  • VUMO
  • Audytplus
  • BKB Kancelaria Prawna
  • CBT
  • Contimax
  • ERBET
  • FOMACH
  • Geotermia Podhalańska
  • LATIS
  • Metgal
  • PIBR
  • Spontex
  • Super Krak
  • Wolimex

Download the ISO/IEC 27001:2022 Virtline certificate

This page combines access to the Virtline document with supplier-assessment support. Click the thumbnail or button to open a PDF scan of the certificate and submit it for a customer audit, partner qualification or compliance documentation. Implementing ISO 27001 in your own organisation is handled as a separate scope.

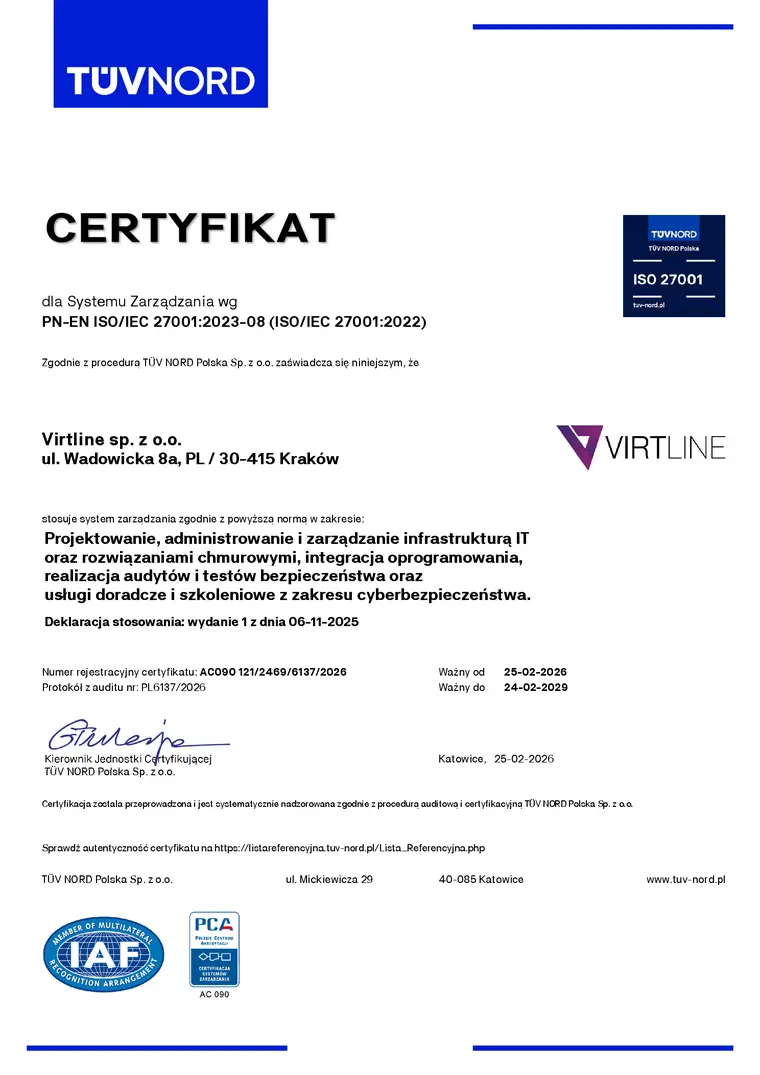
Miniature of the ISO/IEC 27001:2022 Virtline certificate issued by TÜV NORD Polska, valid until 24 February 2029.

Downloadable document

ISO/IEC 27001:2022 Virtline certificate - TÜV NORD Polska

The document confirms the scope of Virtline certification: IT infrastructure, cloud solutions, software integration, security audits and tests, as well as cybersecurity consulting and training.

Certification body
TÜV NORD Polska
Number
AC090 121/2469/6137/2026
Valid from
25/02/2026
Valid until
24/02/2029
Open/download PDF - 480 KB

Virtline’s certificate for supplier assessment

We publish the certificate of Virtline Sp. z o.o. for IT supplier checks, security questionnaires and purchasing documentation. It covers our information security management system; it does not automatically certify your company’s systems.

Go to contact

How a certificate review is performed

Check these four points before adding the document to your purchasing records.

01

Open the document

Use the download button or thumbnail above. It opens the actual certificate scan, not an enquiry form.

02

Check the company

Compare the name and address on the certificate with the legal entity signing your contract.

03

Confirm its current status

Check the number, certification body and dates. The certificate gives the address of TÜV NORD’s reference list.

04

Compare the scope

Assess whether the document covers the service you are buying. Requirements for your own environment, access and responsibilities are agreed separately.

Go to contact

Practical scope

What Virtline’s certificate confirms

The PDF above contains the key details. Compare the certification scope with the service you intend to purchase.

01 Company and certification body

The certificate covers Virtline Sp. z o.o., Wadowicka 8a, 30-415 Kraków, Poland. It was issued by TÜV NORD Polska.

02 Standard and number

PN-EN ISO/IEC 27001:2023-08 (ISO/IEC 27001:2022). Certificate number: AC090 121/2469/6137/2026.

03 Scope of activities

Design, administration and management of IT infrastructure and cloud solutions, software integration, security audits and testing, and cybersecurity consulting and training.

04 Validity period

From 25 February 2026 to 24 February 2029. Check the document’s current status and scope before using it in a supplier assessment.

Go to contact

Questions about Virtline’s certificate

Is Virtline ISO/IEC 27001:2022 certified?

+

Yes. Virtline Sp. z o.o. has the PN-EN ISO/IEC 27001:2023-08 certificate issued by TÜV NORD. Details of the document are available in the PDF file on this page.

Who issued Virtline's ISO 27001 certificate?

+

The certificate was issued by TÜV NORD Polska. The published scan shows the issuer, number, scope and dates; current status can also be confirmed with the certification body.

What does this certificate mean for a Virtline customer?

+

It means that the client works with a supplier whose information security management system has been externally verified, includes IT and cybersecurity services and is maintained in a cycle of audits and reviews.

Does this page describe an ISO 27001 implementation service?

+

The primary scope of this page is to provide Virtline's real ISO/IEC 27001:2022 certificate and support its use in supplier assessment. A client-side ISMS, ISO 27001 gap assessment or implementation is handled as a separate service.

Questions about Virtline’s certificate?

Tell us what information about our security management system you need for supplier assessment. If your enquiry concerns an audit or implementation at your company, describe the intended scope.

Go to contact