
01
Requirements and current state
We review business goals, systems, user groups, dependencies and risks, and identify decision-makers. We agree the budget, licences, constraints and intended outcome.
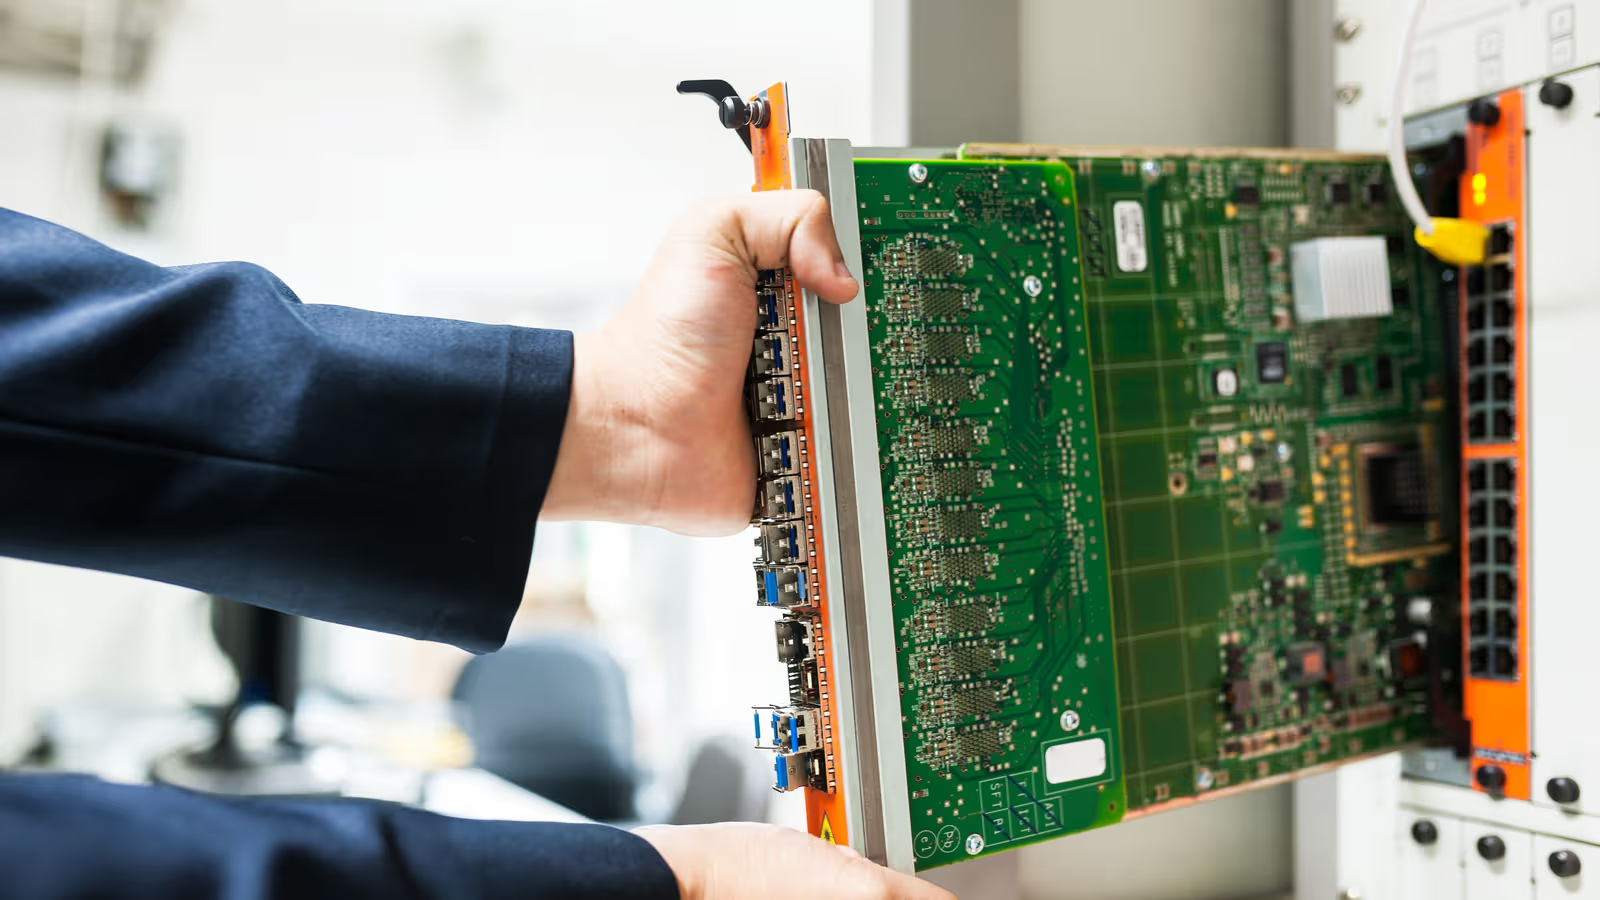
IT implementation projects
We implement and modernise IT infrastructure: servers, virtualisation, databases, networks, identity, email and monitoring. We agree the goal, scope, maintenance windows and acceptance criteria. After launch, we hand over configurations, test results, open risks and a plan for ongoing support.
Trusted by








































A project can cover physical or virtual Windows and Linux servers, file, email, web, application and print services, and FTP/SFTP. We implement Apache, Tomcat, JBoss and IIS, as well as VoIP based on Asterisk, FreePBX or Microsoft Teams Phone. These components connect to networks, Active Directory, Microsoft 365, backups and monitoring. Selection reflects workloads, capacity, licences, budget and business processes, for organisations with a few users through to several hundred.
These pages describe specific project components. A file server does not replace email or applications; their roles and dependencies are defined separately.
TÜV NORD Polska has certified Virtline’s information security management system to PN-EN ISO/IEC 27001:2023-08. The certificate applies to Virtline; it does not establish compliance of the implementation or the client’s organisation.
View Virtline’s certificateFour stages lead from requirements to handover. Downtime, acceptance criteria and responsibilities are agreed before changes.
We review business goals, systems, user groups, dependencies and risks, and identify decision-makers. We agree the budget, licences, constraints and intended outcome.
We prepare the architecture, topology, specification, capacity plan, priorities and schedule. We define data migration, integrations, user communication, maintenance windows, tests and rollback.
We install, configure and migrate the agreed components. We verify operation, access, performance, backups, recovery, monitoring and documentation. We record results and acceptance decisions.
We give administrators configurations, procedures, test results and practical guidance. We agree a stabilisation plan, further reviews and named owners. Ongoing operations require a separately agreed scope.
Practical scope
Acceptance criteria are agreed before work starts. Documentation supports daily administration, management reviews and audits.
Architecture, dependencies, accounts, permissions, policies, logs and changes. For Active Directory, this also covers domain structure, GPO changes and access review results.
Functionality, access, performance, logging and recovery checks within the agreed scope. Recorded results, exceptions, acceptance findings, decisions and open risks.
Administrator instructions, change procedures, maintenance windows, backup coverage, emergency contacts and alert owners. We transfer the knowledge needed to operate the environment.
Post-launch stabilisation, prioritised recommendations and deadlines, development and a support proposal. We agree owners for services, reviews, updates and outstanding work.
The project defines network segmentation, VPN, firewall rules, remote and privileged access, roles and MFA. Secure configuration covers accounts, updates, logs and reduced exposure of services; relevant CIS Benchmarks can provide a reference, not a certification claim. Backups, retention, email archiving and recovery tests are planned alongside acceptable data loss (RPO), service recovery time (RTO) and business continuity. Virtual machine snapshots do not replace backups. Integration capabilities and licensing requirements must be checked for the environment. ISO 27001, NIS2, DORA, KSB 315 and sector requirements may shape the work and documentation; implementation alone does not establish compliance. Setting up monitoring does not mean round-the-clock staffing or an automatic SLA agreement.
Projects can draw on these services. Configuration, incident response and subsequent administration have separately agreed scopes.
Nagios, Zabbix, Grafana or the client’s tool: agreed thresholds, alerts, dashboards and reports. The platform follows requirements and team competence.
Backup architecture, jobs, retention, recovery and testing before production acceptance.
Log sources, security events, priorities and escalation. SIEM integration is distinct from an organised incident response service.
Assessing needs, selecting safeguards, secure configuration, access control and segmentation.
Assessment of organisational gaps and requirements, separate from technical implementation and acceptance.
Administration, monitoring, updates, reporting and minor enhancements after acceptance, under agreed support terms.
Yes. We can implement a single server or service, or an environment for a few, several dozen or several hundred users. A discussion of systems, budget, risks and operations helps define the scope and scale.
Timing depends on the number of systems, data migration, integrations, licences and available maintenance windows. A simple server needs a different plan from virtualisation, databases or VoIP. We agree the schedule after assessing the environment, with stages, acceptance tests and rollback arrangements. Not every migration can be completed without downtime.
We adapt the 30/60/90 plan to the project. By day 30, it covers critical service, access, backup and monitoring checks, initial user feedback, corrections and an exception register. By day 60, it covers performance, capacity, alerts, permissions, documentation and change reviews, removal of temporary exceptions and resolution of acceptance findings. By day 90, it covers a stabilisation report, incident and security reviews, a recovery test, update planning and a decision on further support. Dates and responsibilities are confirmed in the project. IT outsourcing, support for the client’s administrators or recurring reviews can then follow under separately agreed terms.
Yes. Work can include version upgrades, server consolidation, virtualisation, backups, monitoring and documentation. Before migration, we check data, dependencies, integrations, communication plans, possible downtime and recovery options. We also review licences, snapshots and separation of development, test and production environments.
Describe current systems, the proposed implementation, users, business deadline and constraints. We will define scope, dependencies, risks, maintenance windows, responsibilities and acceptance criteria, then prepare a schedule and cost estimate. Do not send passwords or access credentials.
Plan your IT implementation