
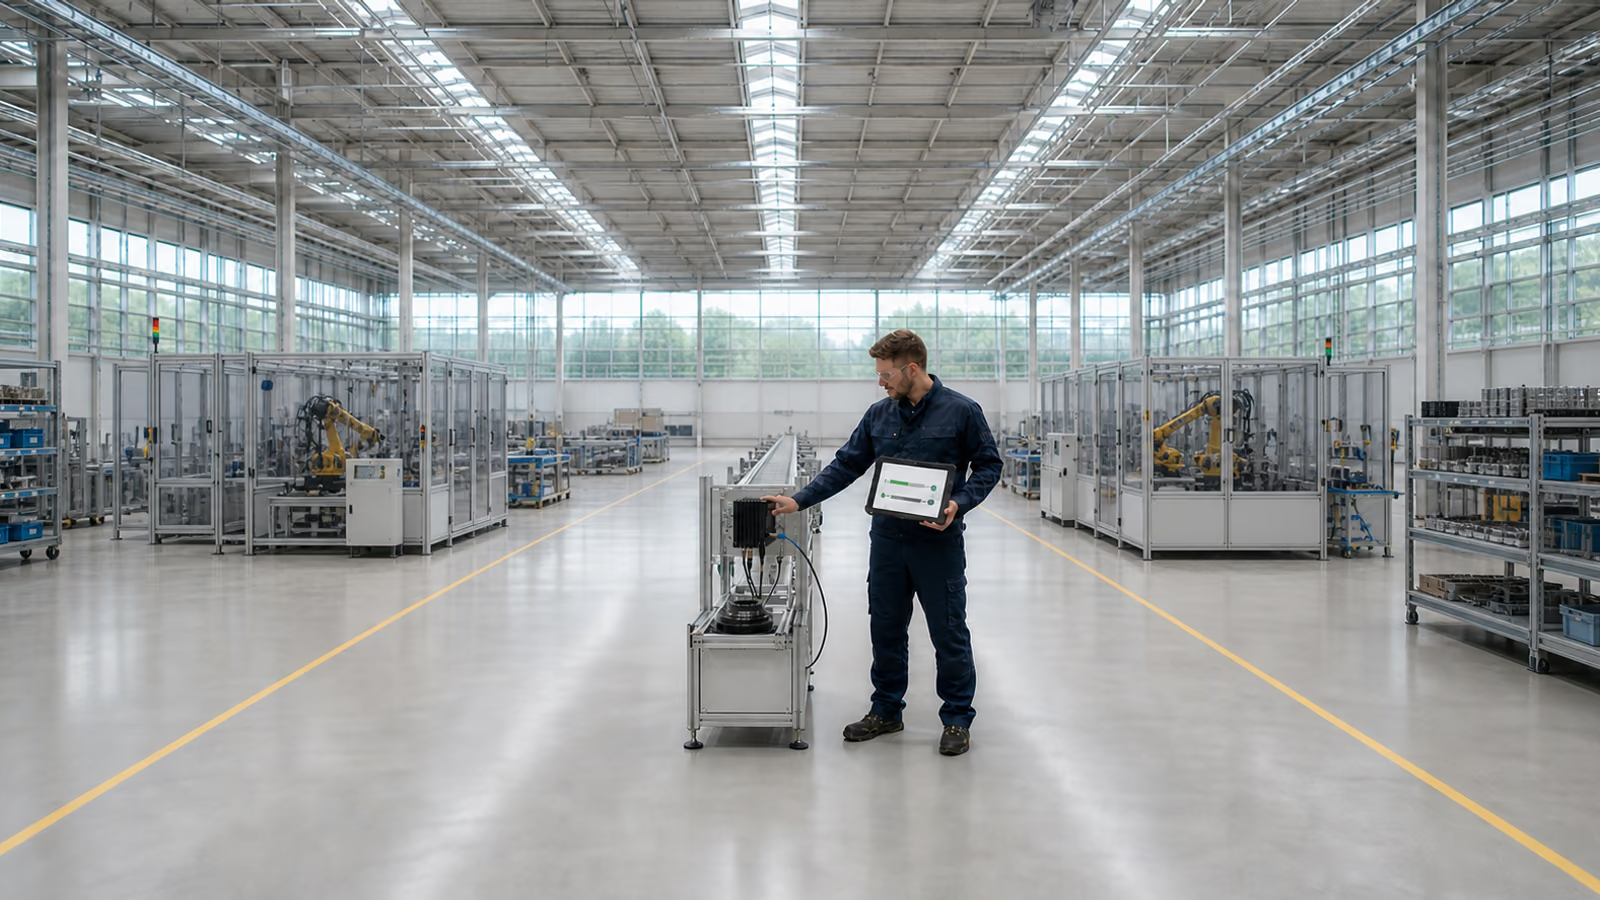
Edge computing — what is edge processing?
Edge computing can reduce cloud load and latency by analysing data near its source. Results depend on architecture, connectivity and node capability. Low latency does not guarantee a fixed response time. It complements cloud and data centres where application, continuity or transfer requirements justify it.
Industry and IoT
Local nodes enable responses to events from machines, sensors and operating systems.
Network and segmentation
Edge requires traffic control, zone separation, VPN and clear administrative-access policies.
Cybersecurity
Every edge node is an additional point that must be updated, monitored and protected.
How processing at the network edge works
Data is analysed, stored and shared as close to its source as possible. An edge node collects information from local devices, structures it and forwards only the required subset to a data centre, cloud platform or reporting system.
- Edge supports IoT, manufacturing, warehouses, branches, video monitoring and processes requiring local response.
- A node may be a server, industrial computer, IoT gateway or embedded system near the data source.
- Initial analysis limits the transfer of large, unprocessed data sets to the central system.
- The architecture requires segmentation, monitoring, updates and clear accountability for local devices.
When edge computing is a good choice
The decision should follow the business process, not a fashion for distributed architecture. Edge is justified when sending everything to the cloud increases latency, transfer cost or the risk of unavailability.
- the system must respond locally when the cloud link is slow or temporarily unavailable
- data from cameras, sensors or machines is too large to transmit in full
- a branch or production floor needs operational autonomy and local analysis
- legal, contractual or security requirements limit transfer beyond the location
- the company wants to retain centrally only data needed for reporting and analytics
Three layers of edge-computing infrastructure
In practice, edge has several levels: sensors, controllers and gateways sit nearest the source; local servers or mini-clusters form the next layer; the data centre or cloud comes last.
Devices and gateways
They collect data locally and must be inventoried, updated and separated from the office network.
Local edge node
It processes data, runs applications and buffers operations during link problems.
Central layer
It receives results, reports and data requiring further analysis, archiving or sharing.
How to collect requirements and define scope
Scope should combine process-owner needs, current systems, incidents, customer requirements, audit findings and budget constraints. Aspirations must be separated from critical functions.
- identify the processes, locations, data sources and applications covered by the change
- define response time, availability and acceptable data-loss requirements
- describe WAN and LAN quality and expected behaviour during their failure
- decide which data remains local and which is sent to the centre or cloud
- assign business, technical and risk-acceptance owners
- define expected evidence, tests, budget and the next review date
How edge computing will develop
Growth will depend on device numbers, transmission cost, response-time requirements and the need to reduce failures at network boundaries. In Industry 4.0, local processing lowers latency and transfer, but requires mature architecture, monitoring and recovery procedures.
Network implementation
The design covers locations, capacity, segmentation and access to edge nodes.
IT monitoring
Nodes need availability, resource, log, temperature and unusual-traffic monitoring.
Backup and recovery
Configurations, cached data and local applications need a tested recovery scenario.
Risks and mistakes that cannot be ignored
Edge distributes the IT environment: there are more devices, sites, updates, network configurations and administrative accounts. Without monitoring and documentation, it is difficult to detect failure, vulnerability or unauthorised change.
- tooling or hardware deployed without a process owner and accountability model
- data copies left in branches without classification and access control
- configuration accepted without testing link loss, node failure and escalation
- operational exceptions without documentation, deadline or business decision
No segmentation
A node must not open an uncontrolled path from production to office systems or the cloud.
No monitoring
Availability, resources, logs, updates, temperature and unusual traffic must be observed.
No recovery plan
Recoverability limits the impact of failure, but restoring data and configuration takes time. Set an RTO and test recovery; uninterrupted service additionally requires appropriate redundancy and tested failover.
Secure operation of edge nodes
Distributed nodes require the same access control, updates and observability as central systems, while also coping with constrained connectivity and physical access at a remote site.
Edge-node monitoring
Availability, load, connectivity, versions and errors have a clear alert owner.
Security and maintenance model
Segmentation, identity, updates and failure response are designed before devices are installed.
A phased action plan for an edge project
A sensible rollout starts with the process and risks, followed by devices, platform, segmentation and operations. The following 30/60/90-day schedule is illustrative. Required safeguards, link-loss behaviour and node recovery must be tested before production acceptance.
- 30 days: choose a process requiring low latency and describe its data, sources, locations and availability.
- 60 days: design the network, segmentation, updates, administrative accounts, configuration backup and monitoring.
- 90 days: run the pilot and test link loss, node recovery, incident escalation and reporting to the process owner.
- decide what data stays local and what is sent to a data centre or cloud
- incorporate edge into existing security, backup and ticket-handling procedures
The implementation process step by step
The project should move from diagnosis to operations, separating quick corrections from changes requiring budget or a management decision.
- diagnose the process, systems, data flows and network dependencies
- assess risks, availability requirements and site constraints
- design the target with segmentation, identity, monitoring and backup
- pilot at a controlled site with success and rollback criteria
- test link, node and power failures, recovery and incident escalation
- hand over to operations with documentation, training and a decision report
Evidence and documentation after implementation
Documentation must preserve quality after the project and demonstrate control during an audit, customer review or supplier change.
- approved scope and a map of locations, systems and data flows
- architecture decisions, configurations, versions and settings backup
- business and technical owners together with a responsibility matrix
- test results for availability, link loss, recovery and incident response
- exceptions, open risks, acceptance decisions and deadlines
- operating, update, monitoring and device-handling procedures
- next review date and metrics reported to IT and management
How to measure and report effectiveness
Management reporting should separate technical facts from business decisions. It shows the effect on continuity, security, cost and audit readiness rather than merely counting completed tasks.
- node availability, local response time and number of process interruptions
- time to detect and handle a failure, alert or unauthorised change
- results of recovery tests and operation during central-link loss
- number, age and owners of open exceptions and risks
- link usage, volume of data retained locally and transfer cost
- completeness of documentation, reviews and assigned accountability
Management decisions and compliance requirements
Management approves risk appetite, budget, priorities and permitted exceptions. ISO 27001 is a standard for structured security management and evidence. Determine NIS2 and DORA duties under their applicable entity scope and rules; using an edge architecture alone does not establish that either regime applies.
- which processes and data must remain available without cloud connectivity
- what recovery time and level of data loss are acceptable
- who funds links, redundancy, hardware, monitoring and local support
- which exceptions require formal acceptance and compensating controls
- what evidence must be available to management, auditors, customers and regulators
Supplier discussion and acceptance criteria
A supplier should speak in terms of outcomes, risks and evidence, not only features. Acceptance does not end with confirmation that a device works on installation day.
- clear responsibility for the network, node, application, data and updates
- test scenarios for failure, recovery, link loss and unauthorised access
- configuration documentation, knowledge transfer and exception handling
- agreed response time, escalation, maintenance cost and spare-part availability
- proof that monitoring, backup, segmentation and identity controls operate
- a review plan after 30 or 90 days of production use
How to maintain control after rollout
Controls lose value as infrastructure, applications, users and suppliers change. Edge needs an operating rhythm that triggers an additional review after a significant business or technical change.
- review configurations, permissions, alerts and device versions regularly
- test configuration backup and recovery of local applications and data
- update the flow map, documentation and owner list
- control physical access to devices in branches and external locations
- include exceptions and material deviations in periodic management reports
- repeat tests after a link, application, supplier, firmware or topology change
How Virtline can help
Virtline assesses the business case for edge computing, designs a secure network, configures monitoring and brings local nodes into an ongoing IT service model.
Computer networks
We design segmentation, VPN connections, routing and traffic rules between sites.
IT monitoring
We configure availability, resource, log, alert and critical-component monitoring.
IT outsourcing
We take over maintenance, documentation, reporting and periodic environment reviews.
Related articles
Edge computing combines network architecture, monitoring, business continuity and alignment of technology with the business process.
Adapting technology to business requirements
How to select technology for the process, risk, cost and company development plan.
Modern IT solutions for companies
How to select solutions that improve applications, systems and business continuity.
IT network management in the company
Network-control fundamentals that also matter in edge and IoT environments.







































